Roles, limits and security
An AI assistant acts with the rights of the user who connected it, never with more. In addition, the administrator decides per person whether the assistant may only read or also write, execute and build, and per account how much is allowed within an hour and which actions need an approval. Every decision is made by Pantarey on the server and logged. What the assistant itself "promises" is irrelevant for security.
The roles
Assigned under Users → Manage users → Permissions. The add-on roles only work together with the first one.
| Role | Effect |
|---|---|
| Connect external AI assistants (MCP) | Connection allowed. The assistant reads: data, analytics, processes, tasks, dashboards. |
| External AI assistants (MCP): write records directly | Additionally: create and change records. |
| External AI assistants (MCP): start processes and complete tasks | Additionally: start processes and complete tasks. |
| External AI assistants (MCP): build (developer mode) | Additionally: create data schemas and change their fields, rules and permissions, create and build processes, change dashboards. Only works while developer mode is on, see Building with the assistant. |
"Processes only" mode: If only the third role is assigned, the assistant can change data exclusively through the processes the company has defined, for example "Create contact" with the checks built into it. Editing records directly is not possible then.
Administrators do not get any of these roles automatically. For them, too, the access is a deliberate decision.
Rights from the app still apply
- Data schemas: Permissions from the Data Designer (list, read, create, update, query) apply to the assistant in the same way. A record from a schema without read permission is not delivered, not even as a reference inside another record.
- Separate rights for AI assistants: Each permission can define that the assistant may do less than the user in the app, for example read a schema in the app but not in the chat. The default is "same as in the app". More under Permissions for AI assistants.
- Only certain records and denies: If a user may only see certain records of a schema, the assistant also sees only those. Lists and counts then refer to these records only, and the assistant says so. Denies apply to the assistant in the same way. More under Only for certain records and Denies.
- Processes and tasks: Only start events and tasks assigned to the user or one of the user's groups can be started or completed.
- Analytics: SQL queries run only over tables for which the user has the permission "Query". If the user may only see certain records of a schema, SQL queries also return only those. System tables (
prio_…) can be queried by administrators only. - Building: The assistant builds only what the user could build themselves: data schemas in the Data Designer, processes in the Process Designer, dashboards in the Dashboard Designer.
- Deleting: The assistant never deletes records, processes or cases. In developer mode it can delete individual fields and permissions of a data schema, each with a dry run and, by default, with an AI approval.
Limits & switches
Under Users → AI assistants → Limits & switches, the following applies to the whole account:
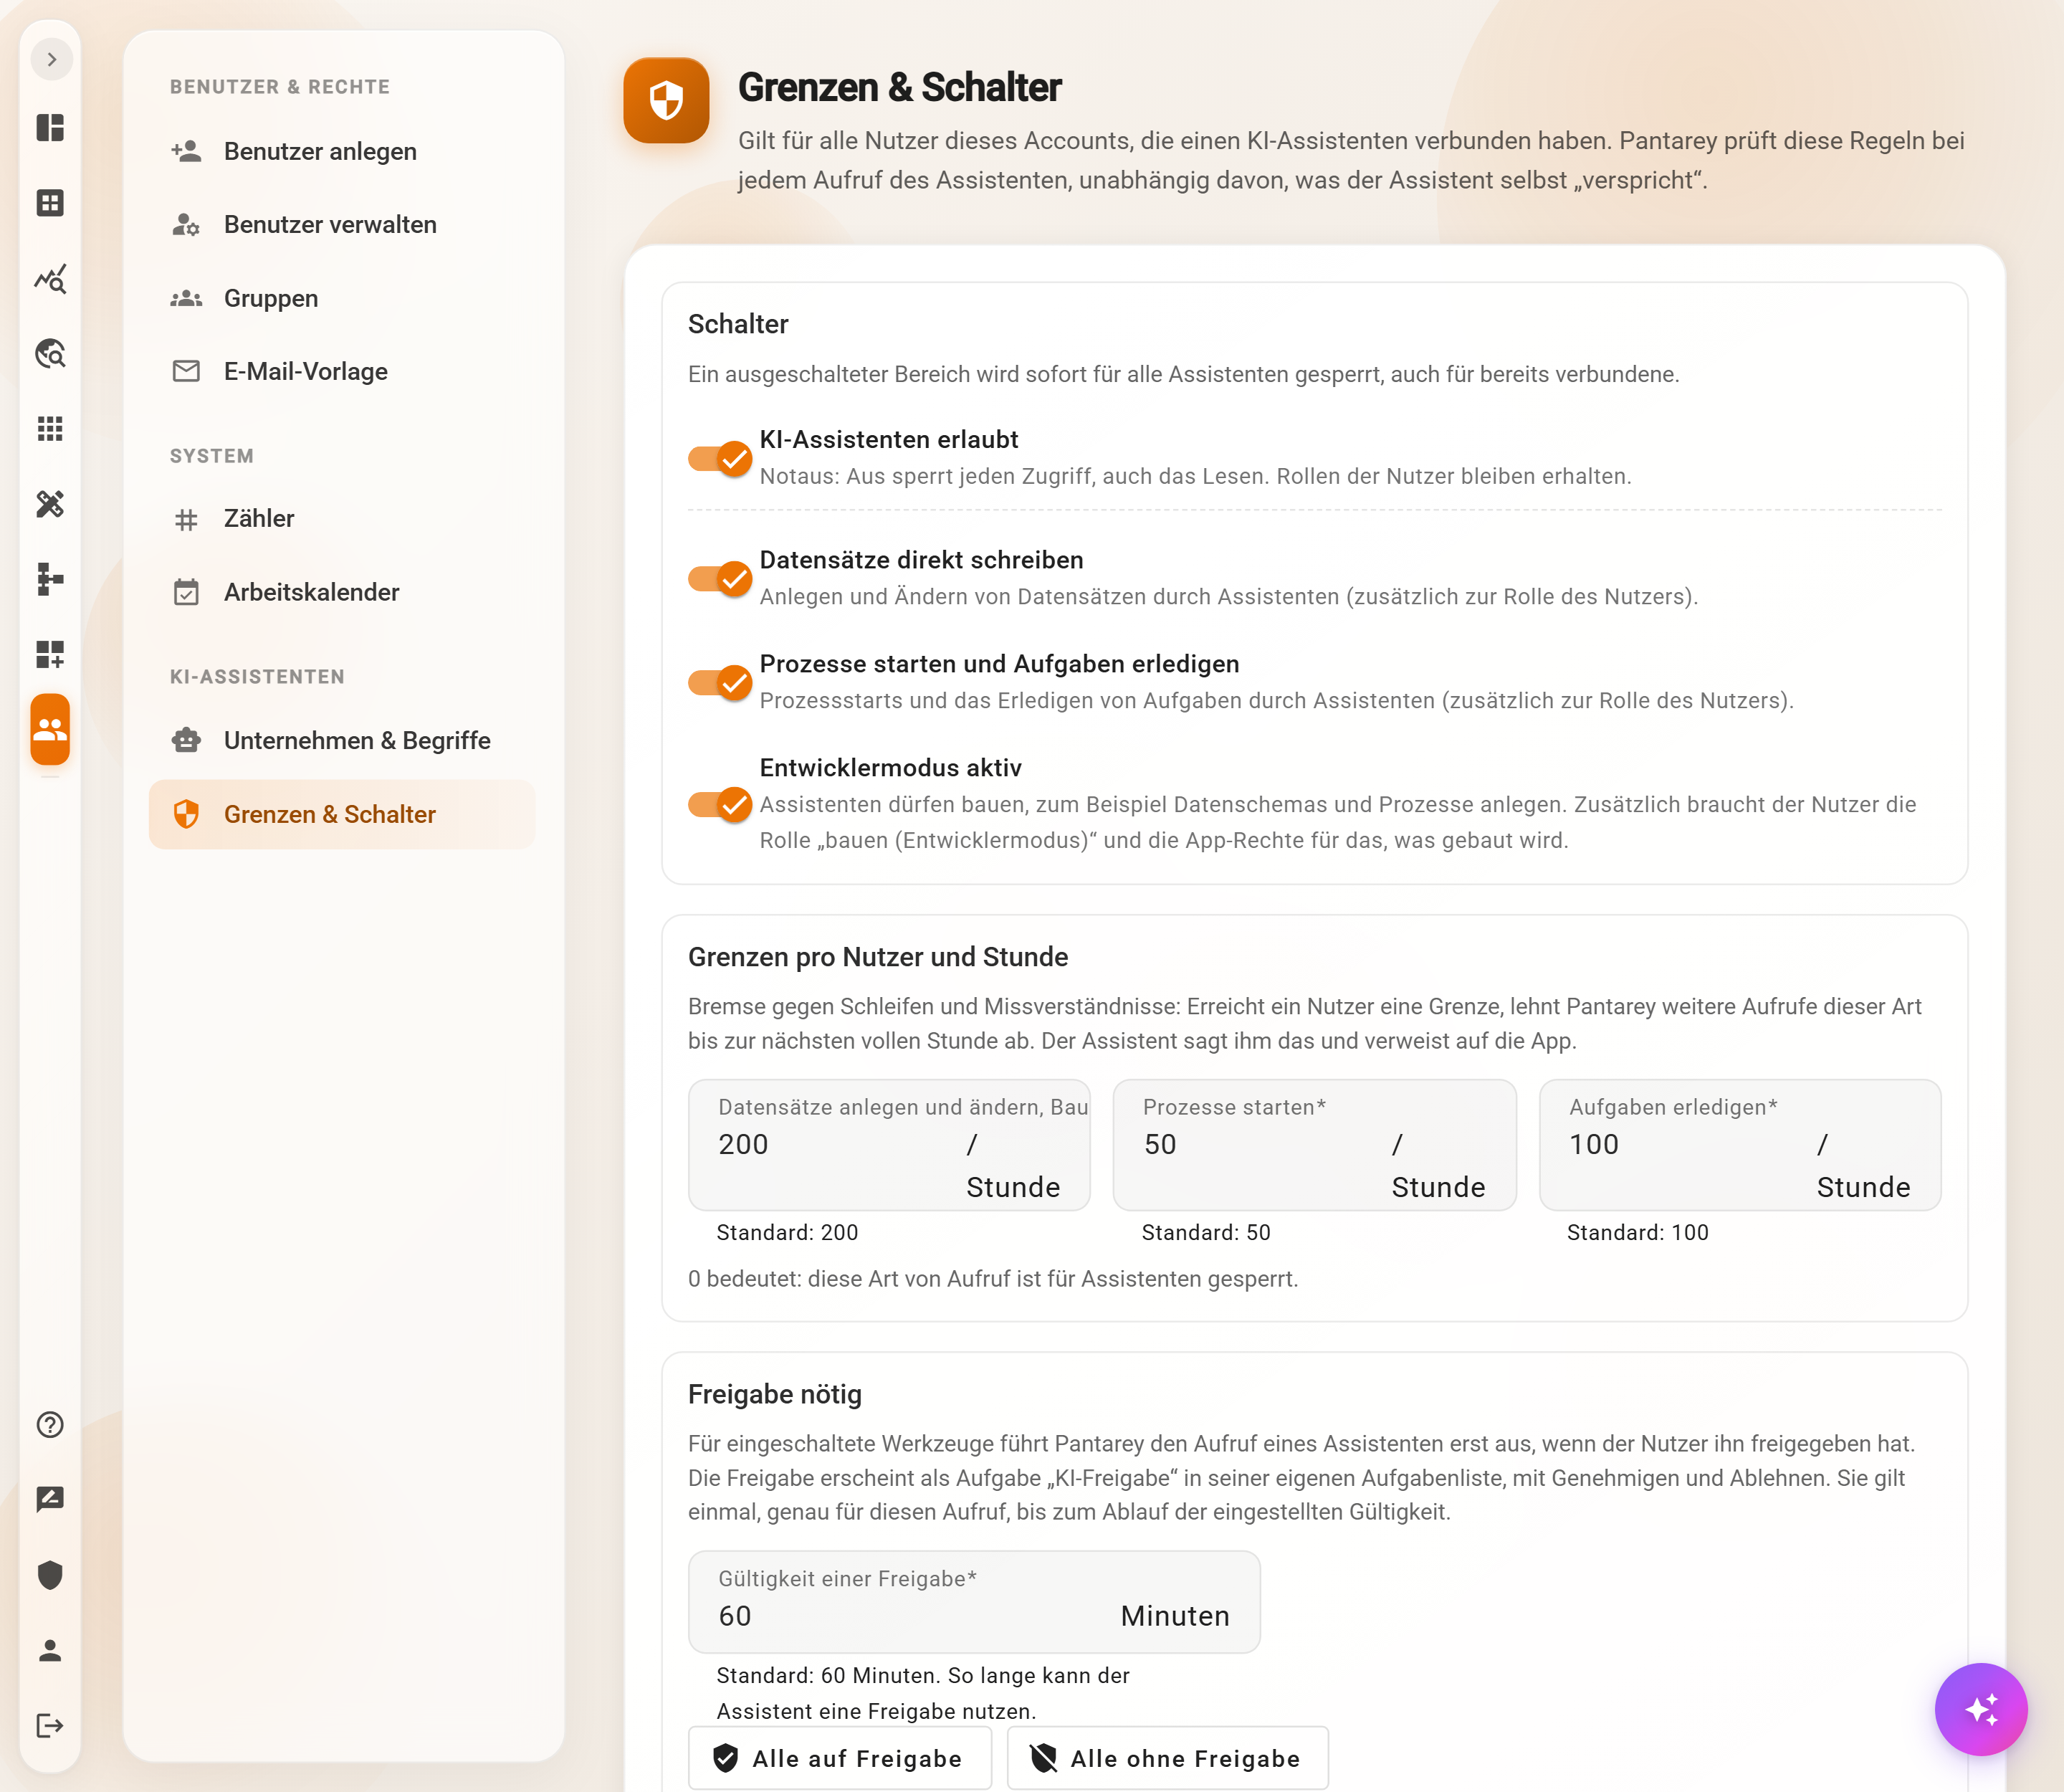
Switches
- AI assistants allowed: The main switch, off by default. An administrator switches it on once before assistants can be used. Off means: no access, not even reading; connected assistants no longer see any tools. Roles are kept, which makes the switch the kill switch as well.
- Write records directly: creating and changing by assistants, in addition to the user's role.
- Start processes and complete tasks: in addition to the user's role.
- Developer mode active: Assistants may build, for example create data schemas and processes. Off by default. The user also needs the role "build (developer mode)" and the app rights for what is built.
A switched-off area is blocked immediately for all assistants, including those already connected.
Limits per user and hour (defaults in brackets)
- Create and change records, building (200)
- Start processes (50)
- Complete tasks (100)
The limits are a brake against loops and misunderstandings. Once a user reaches a limit, Pantarey refuses further calls of that kind until the next full hour. The assistant says so and points to the app or the administrator. Counting uses fixed hour windows (full hour, UTC). The value 0 blocks that kind of call.
When the assistant creates several records at once, every record counts separately. A batch is only accepted if it fits completely into the remaining limit; otherwise nothing is created and nothing is counted, and the assistant learns how many are left. Dry runs never count.
Approval required
For each tool, it is set whether a call runs only after the user's AI approval. The approval appears as an "AI approval" task in the user's own task list, with Approve and Reject, and is valid once, for exactly this call, until the set validity runs out (5 to 1440 minutes, default 60). Out of the box, only creating data schemas and changing fields, rules and permissions need an approval; processes and dashboards are taken over in the designer instead. Creating records or starting processes can be set to require an approval as well. Details under AI approvals.
Changes take effect immediately for all users of the account.
Log
Every call of an assistant is recorded in the table prio_mcp_usage_statistics in Data analytics. Only administrators can query it, like all system tables whose name starts with prio_.
| Column | Content |
|---|---|
user_email, client |
Who, with which assistant |
tool |
Which tool |
result |
ok, rejected, denied (no permission), invalid, error |
decision, guard |
Decision of the check (allow, approval_required, deny) and which check made it (switches, approval, precheck, budget, permission) |
target_ids, produced_id |
Affected ids and, for writing calls, the created id |
approval_id |
The AI approval the call requested or used |
policy_version |
Version of limits & switches at the time of the call |
duration_ms, execution_timestamp |
Duration and time |
Record contents or SQL texts are not logged, only a hash of the arguments.
Example query:
SELECT execution_timestamp, user_email, tool, result, decision, guard
FROM prio_mcp_usage_statistics
ORDER BY execution_timestamp DESC
LIMIT 50
Example
An employee is supposed to analyze invoices via chat but change nothing. He only gets the role "connect". His assistant can search, read and run SQL queries. If he tries to create a record, the tool for it simply does not exist.
Frequently asked questions
How is access introduced step by step?
First assign only "connect", look at the log after a few days, then writing roles for individual people. Developer mode can be switched on for the duration of a project and off again afterwards.
What to do when misbehaviour is suspected?
Switch off AI assistants allowed: this blocks every access immediately, including reading. Then check the log and withdraw a role deliberately. The roles are kept when the kill switch is used.
How can one tell that a limit is too low?
In the log by guard = budget and result = rejected. The column tool shows which kind of call was affected; the corresponding limit is then raised.
Does the assistant see other users' data?
Only if the connected user also sees it in the app. There is no collective access; every assistant is bound to exactly one user account.
Next step
Company & terms: explain the company to the assistant so that it understands the users' words correctly.